Full Protection,
Zero Complexity
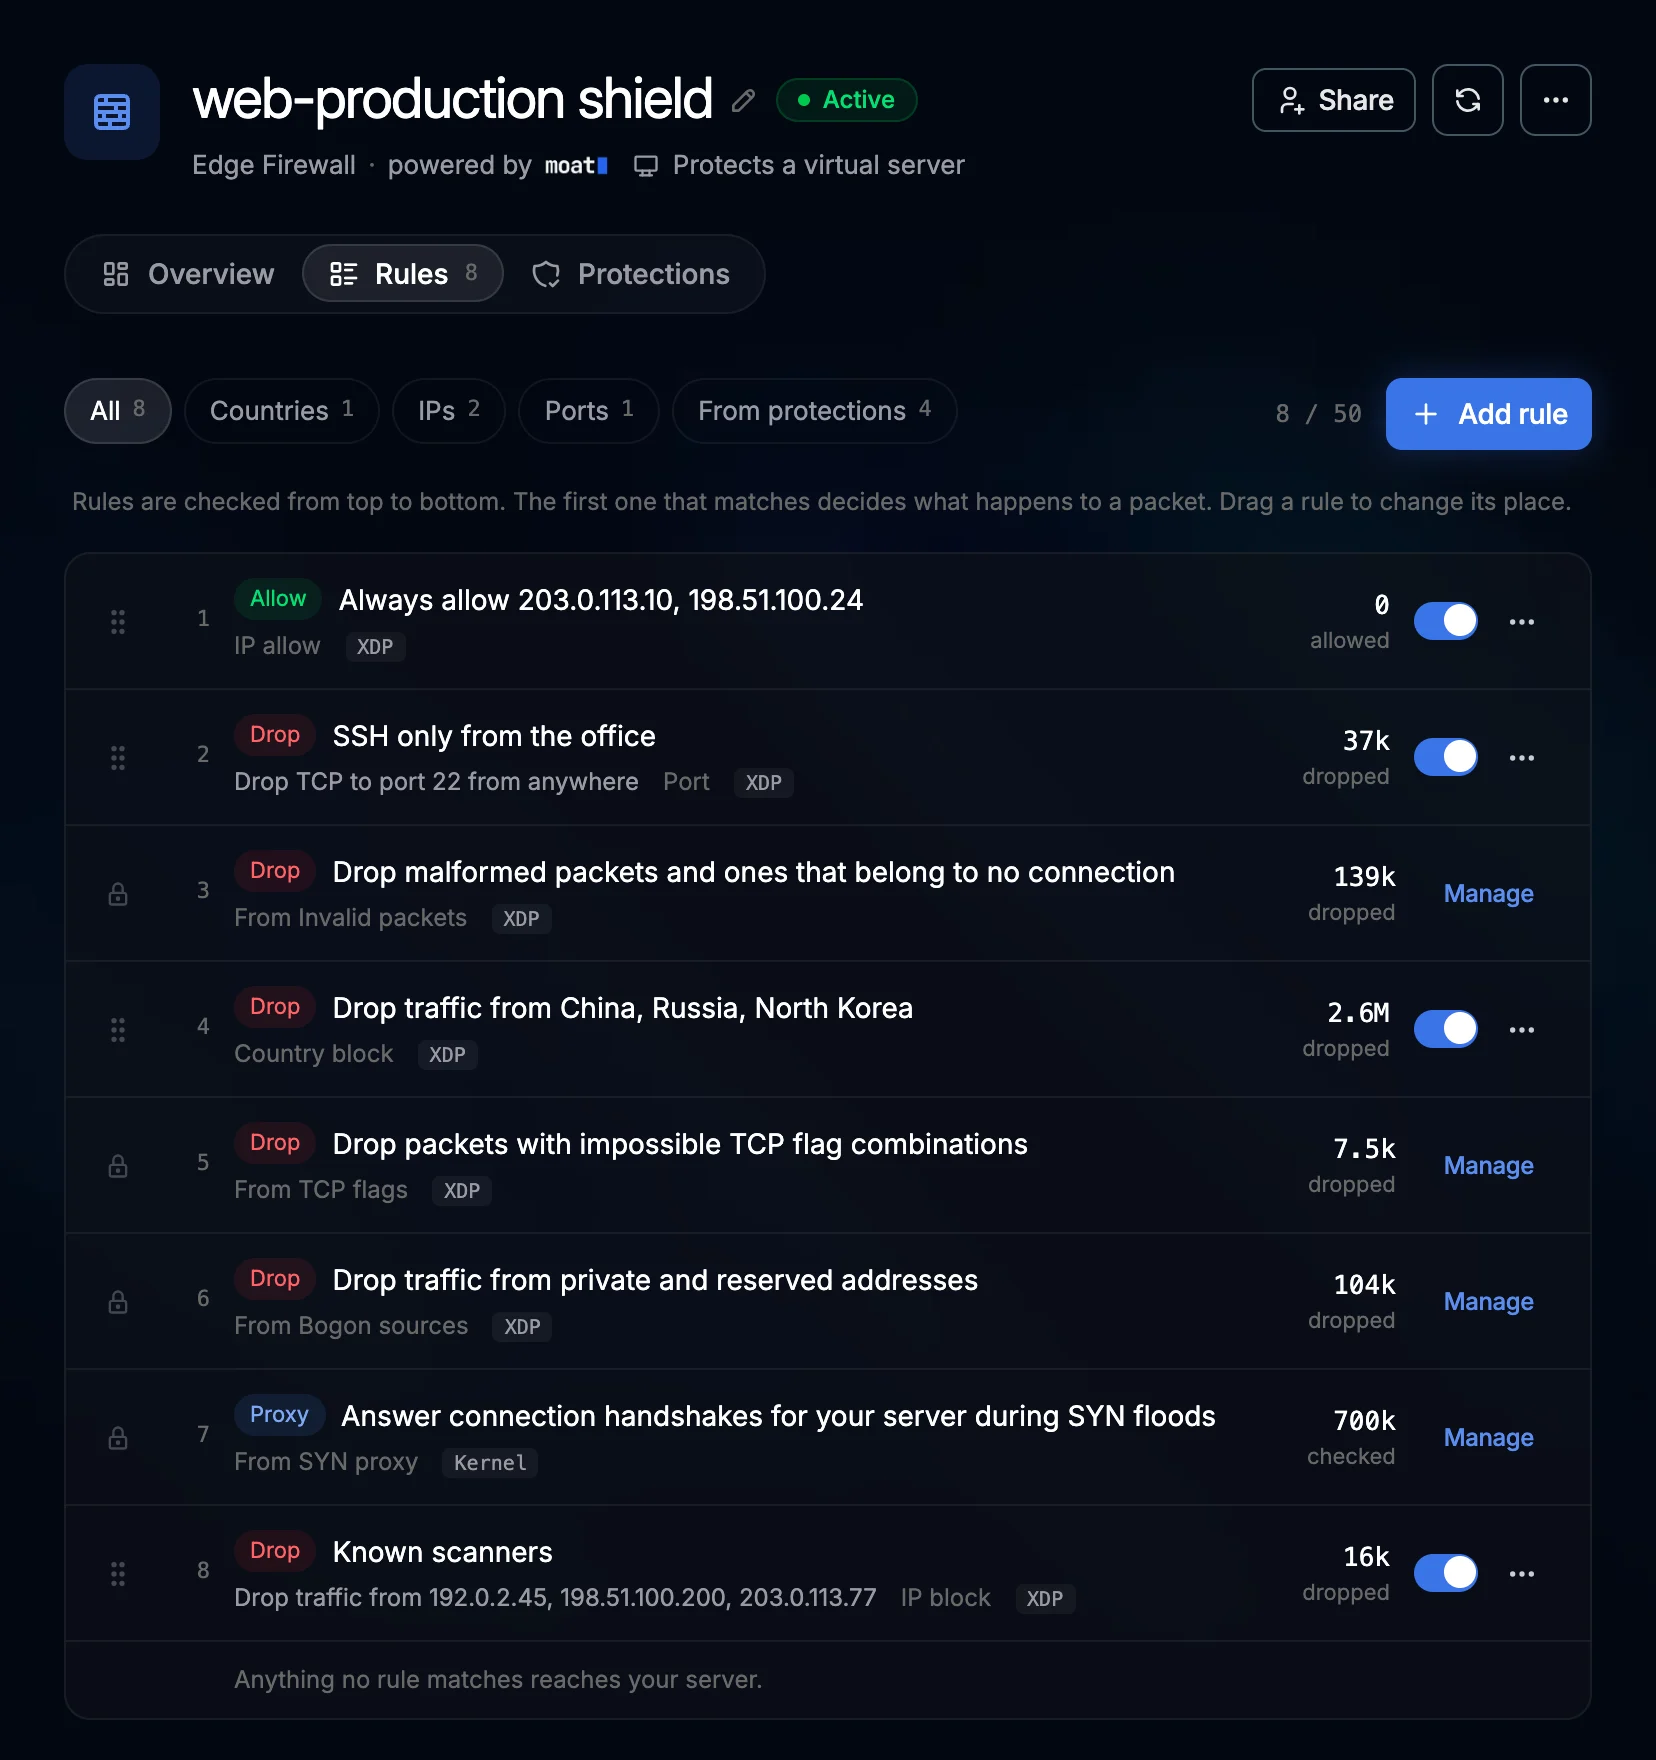
You don't need to be a network expert. Toggle pre-built profiles, manage rules from your panel, and get real-time attack intelligence, all without touching a terminal.
UDP Flood detected and dropped at the edge
How it works
Attacks are dropped before they cost your server anything.
- 01
Traffic arrives
Players, users and attackers all reach the network card of the host your VPS runs on.
- 02
moat decides in XDP
Your rules run in the network driver and drop or rate limit each packet. moat follows connections itself, so only the SYN proxy runs after it, in the kernel.
- 03
Clean traffic reaches you
Only what your rules allow gets to your VPS, so floods never use its CPU or bandwidth.
Our own XDP technology. moat is the open source rule language PlaySafe built for this firewall.
Compiled to XDP
Rules run in the network driver, before the Linux network stack sees the packet. Only the SYN proxy runs later, in the kernel.
Tested before it loads
Rules can be run against test packets before they load, so a mistake is caught before it reaches a server.
Open source
moat is developed in the open. Read the language, the compiler and the examples on GitHub.
Apache-2.0 licensed. See how moat handles common attack patterns in the examples repository.
Two clicks, full protection
Turn on a profile and you are protected. Need more control? Write your own rules.
Close Access
Locks the server to your own IP and allowlist
TCP Flag Protection
Drops impossible SYN, RST and ACK flag combinations
Invalid Packet Drop
Drops packets that belong to no valid connection
Bogon IP Protection
Blocks private and reserved source ranges
Fragment Drop
Stops IP fragmentation attacks
ICMP Rate Limit
Mitigates ICMP flood attacks
SYN-Only Connections
New connections must start with a handshake
MSS Validation
Filters suspicious or missing TCP segment sizes
RST Rate Limit
Rate-limits TCP reset storms
SYN Proxy
Answers handshakes for your server during SYN floods
Connection Limit
Caps open connections per source IP
TCP Rate Limit
Limits new connections per second
UDP Rate Limit
Controls UDP traffic rates
SSH Brute Force
Blocks repeated SSH login attempts
Port Scan Protection
Detects and blocks port scanning
Payload Match
Drops packets whose payload contains a pattern you choose
Know about every attack
A live alert when it starts, a report when it ends, and a message wherever your team is.
Live alerts
Traffic checkpoints, attack vectors, origin map and an AI summary, with three severity levels.
PDF post-mortem
Every resolved attack gets a downloadable report.
- Executive Summary
- Tactical Analysis
- Attack Vectors
- Traffic Timeline
- Origin Breakdown
- Recommendations
Notifications
- Discord. Alerts with severity, vectors and a link to the panel.
- Email. When an attack starts and when it is resolved.
- Reports. Weekly, biweekly or monthly summaries.
Your server, your rules
Deploy your edge firewall in minutes. Toggle profiles, create rules, and let the alerts tell you what's happening, no network expertise required.
Deploy Firewall